A note before you begin: in some regions the 1xBet app does not appear in official stores due to local regulations. The instructions below cover the direct APK route, which remains fully functional when store access is restricted.
Preparing Your Device and Choosing Your Source
Installing third-party Android software demands a moment of deliberate setup. Your phone’s security model treats browsers and file managers as separate installation sources, each requiring independent permission grants. This granular approach protects you; it also means you must remember which app initiated your download, as revoking permissions later follows the same path.
Begin with these checks:
- Verify your phone has sufficient storage for the APK and its extracted data
- Confirm your Android version supports modern package installers
- Identify whether your browser or a dedicated file manager will handle the download
- Locate your Settings path to “Install unknown apps” for that specific source
- Decide now whether to enable automatic updates or manual verification
This preparation prevents the common trap of hunting through nested settings menus mid-installation. The permission architecture changed significantly across Android generations, so older guides may mislead. Current systems assign unknown-source rights per-application, not globally, and you retain the option to revoke these rights after installation completes.
Obtaining and Placing the APK File
Download practices shape your long-term security posture. The 1xBet Android package arrives as a single compressed file with the .apk extension, which your system unpacks during installation. Your download destination matters: browsers typically place files in a Downloads folder, while some file managers allow custom paths that simplify later location.
Follow this sequence:
- Initiate the download from your chosen source while connected to stable internet
- Allow the transfer to complete fully; partial files install incorrectly
- Note the file name and timestamp to verify completion
- Keep the file accessible but avoid opening it immediately
- Pause to check the download source against known distribution points
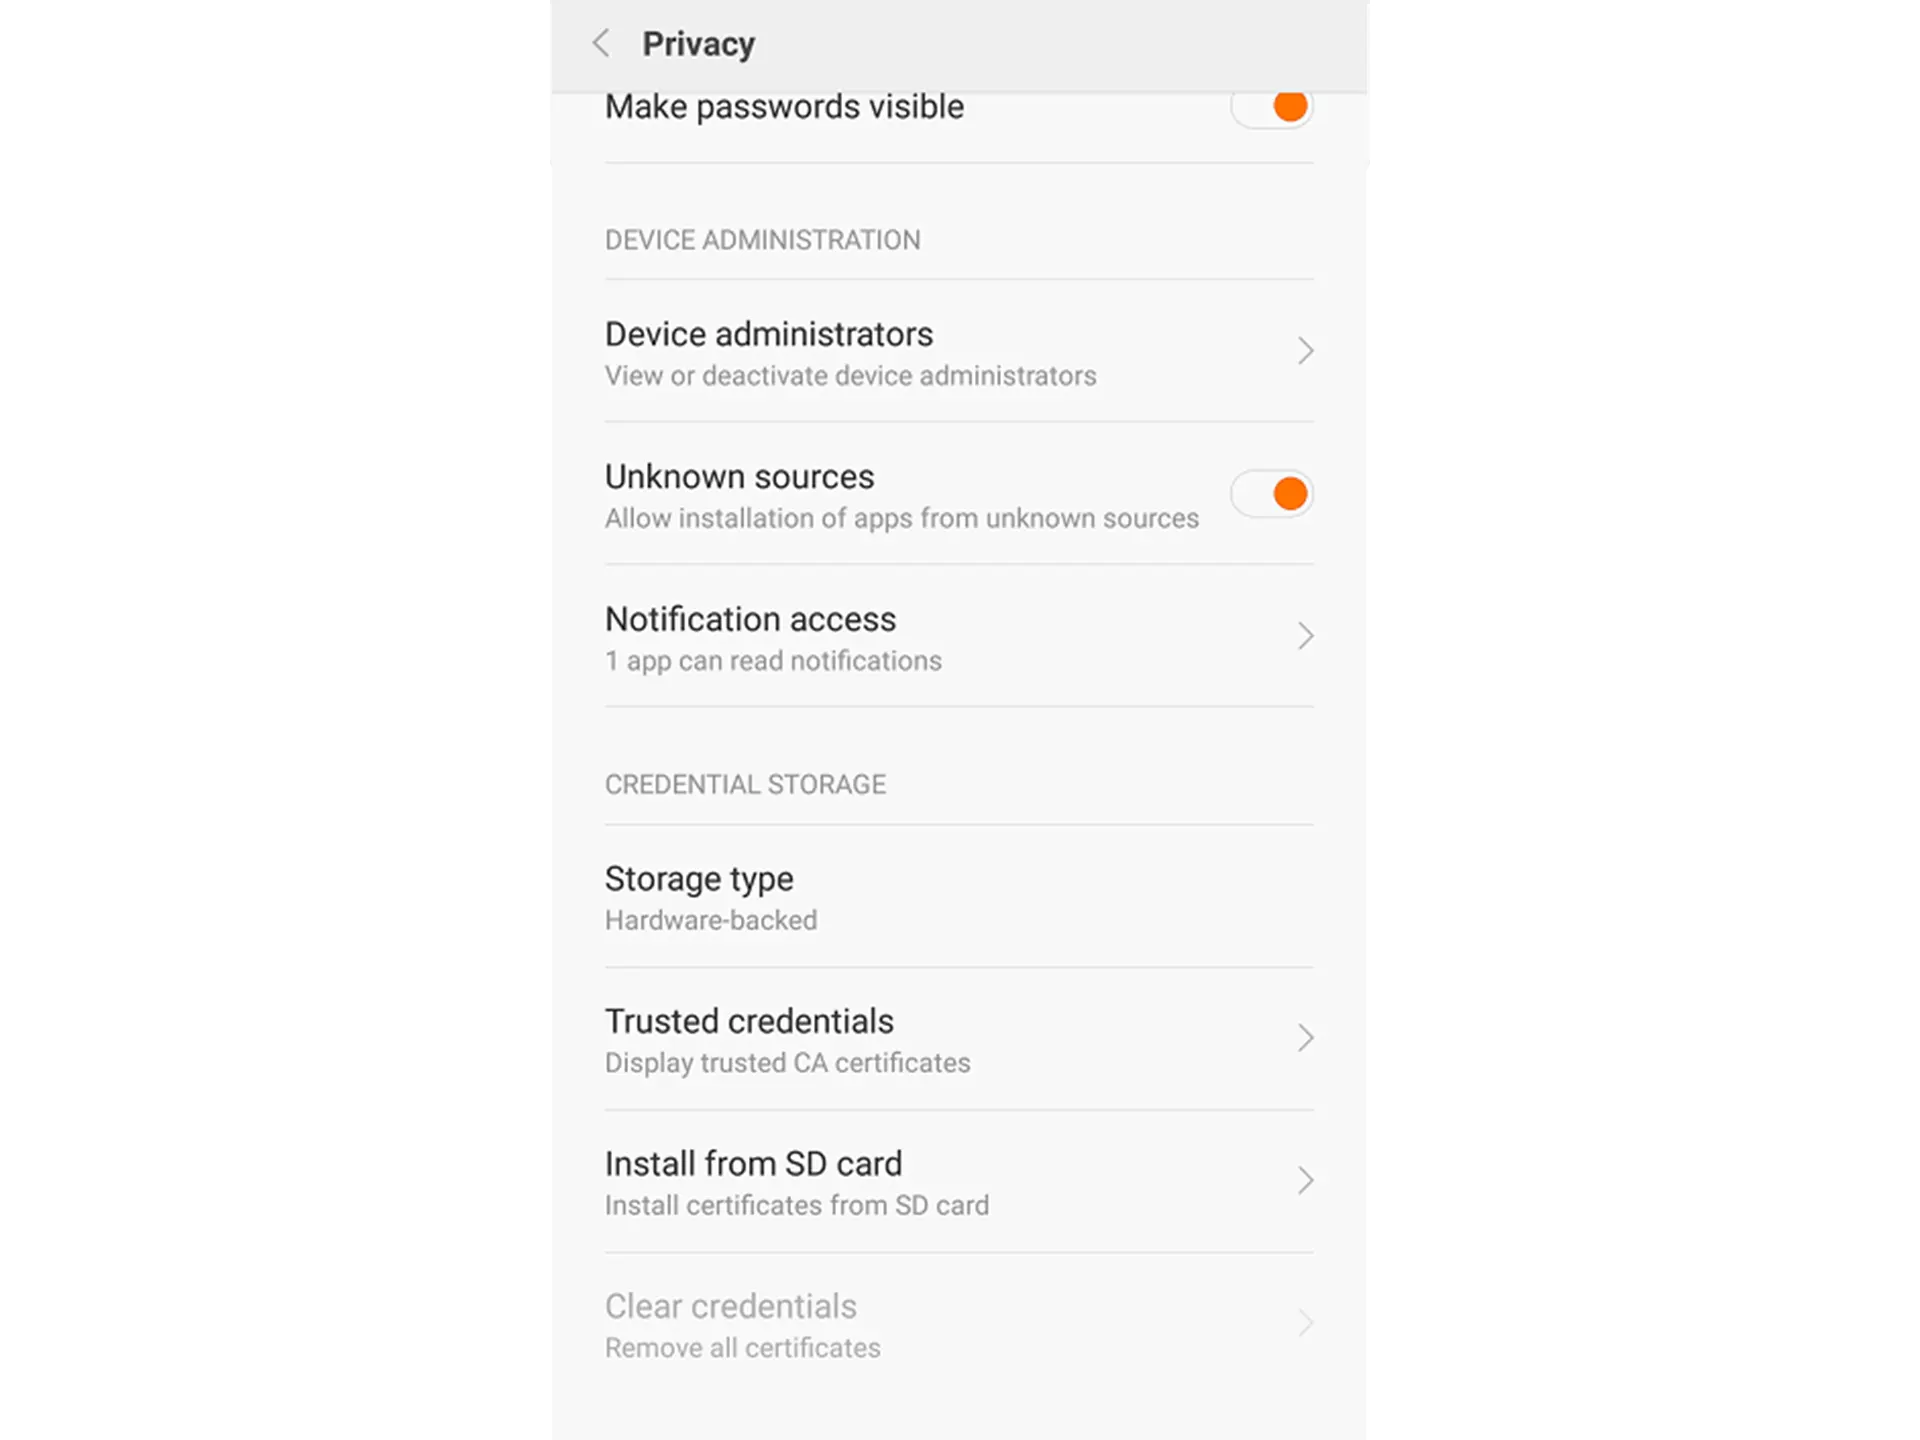
The release channel and regional availability determine how the 1xbet android package mobile version distributions vary across different markets and update schedules. Cross-checking file hashes where provided adds verification depth, though this step sits outside basic setup. The core principle: treat your download source as a decision that persists across years of app updates.
Installation, Permissions, and Post-Setup Security
Android’s installation flow now guides you through source-specific permissions automatically. When you tap the APK, the system detects whether that source holds installation rights and offers a direct path to grant them if absent. This replaces the older global “unknown sources” toggle with precise, reversible controls.
| Step |
Action |
System Response |
| 1 |
Tap the downloaded APK |
Package parser validates file integrity |
| 2 |
Grant source permission if prompted |
Settings opens to correct app-specific toggle |
| 3 |
Confirm installation |
Progress bar indicates extraction and placement |
| 4 |
Complete setup |
Launcher icon appears; optional: revoke excess permissions |
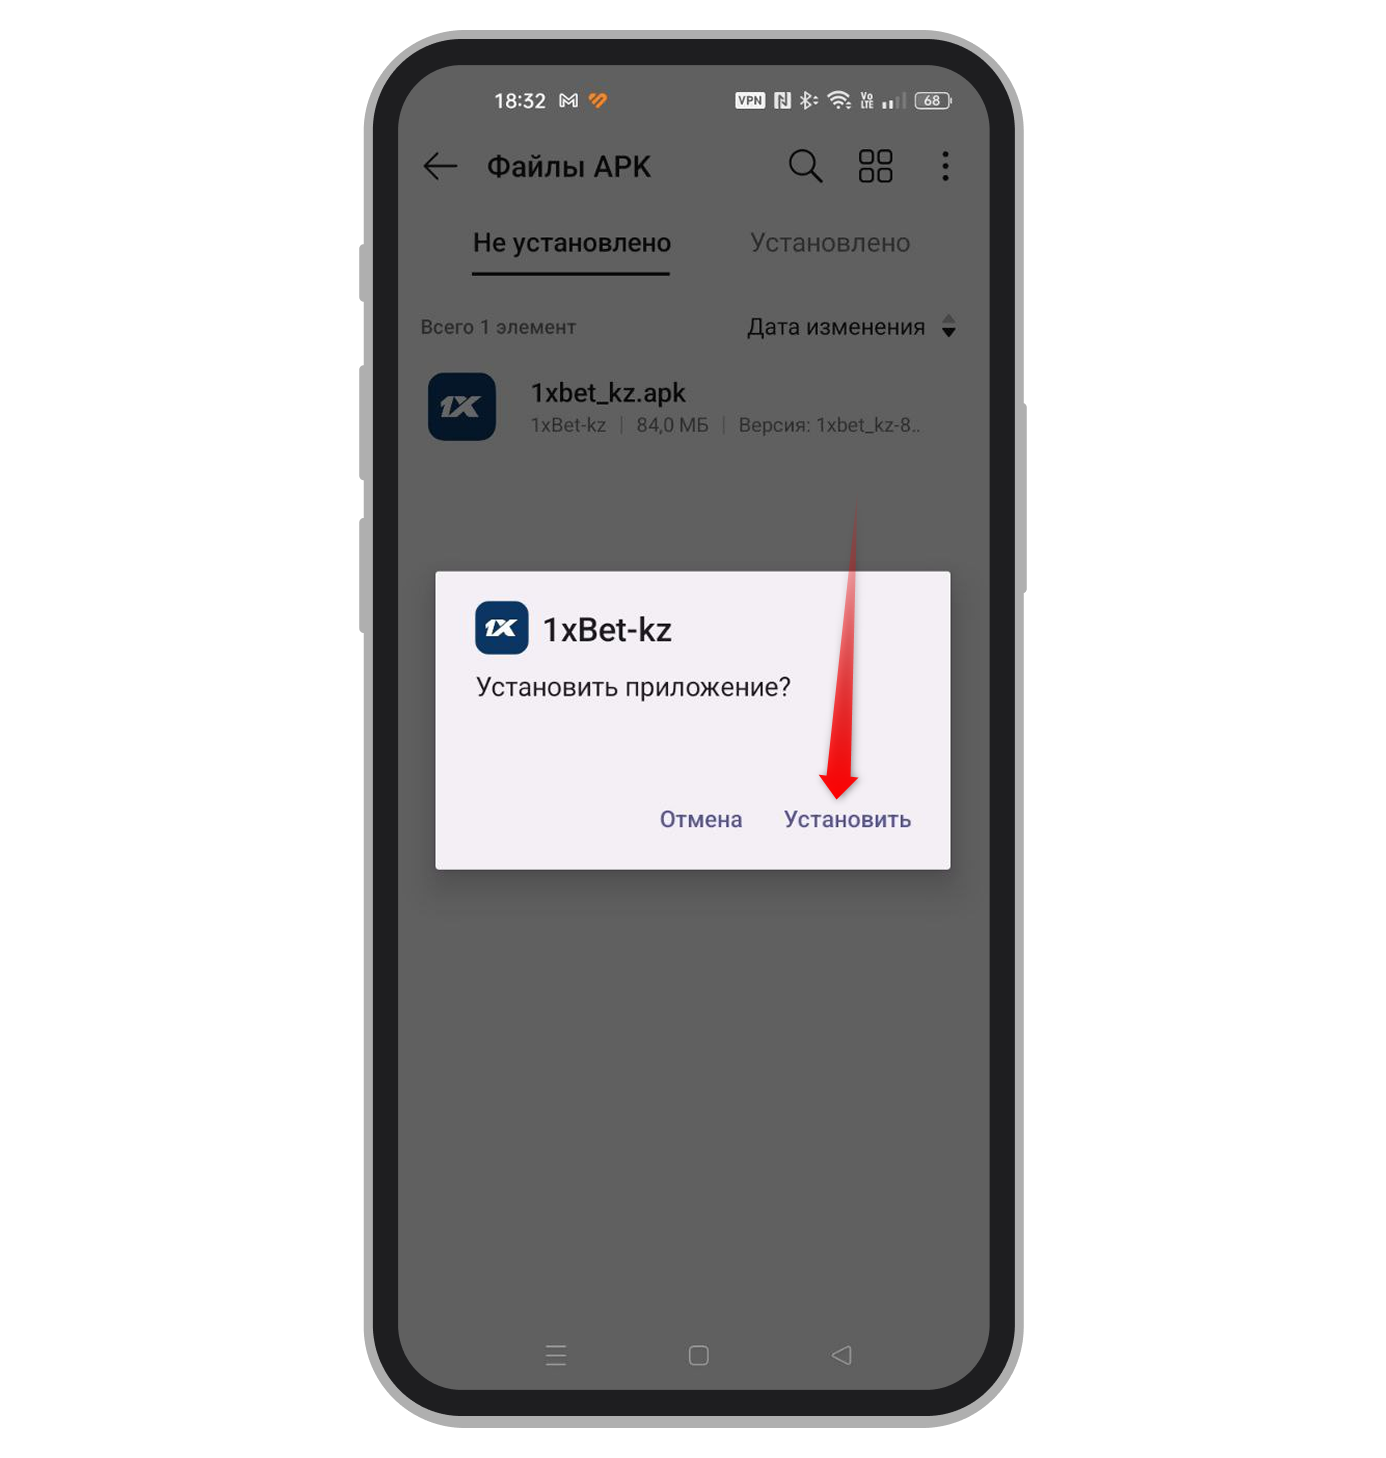
Post-installation, consider your permission footprint. The browser that fetched your APK no longer needs installation rights; revoking this closes a potential vector without affecting the installed app. Similarly, the 1xBet application itself requests runtime permissions for notifications, location, and storage—grant these selectively based on your actual usage patterns rather than accepting defaults.
Update handling requires attention to certificate continuity. Android refuses updates signed by different certificates than the original installation, forcing an uninstall-reinstall cycle that may clear local data. Maintaining awareness of your original download source prevents this disruption. When updates arrive, verify the signing identity matches your baseline before applying.
Core Capabilities and Platform Architecture
The application presents a consolidated interface spanning multiple verticals without forcing navigation through separate installations. Sports betting occupies the primary real estate, with pre-match odds and live-event pricing accessible through shared search and filter tools. The live betting module updates prices in response to match events, with cash-out availability varying by sport and market liquidity.
Casino integration runs parallel rather than as an afterthought. Slots, table games, and live dealer streams pull from the same account balance and loyalty tracking. This unified wallet architecture eliminates the friction of inter-product transfers, though responsible gambling limits apply across all verticals simultaneously.
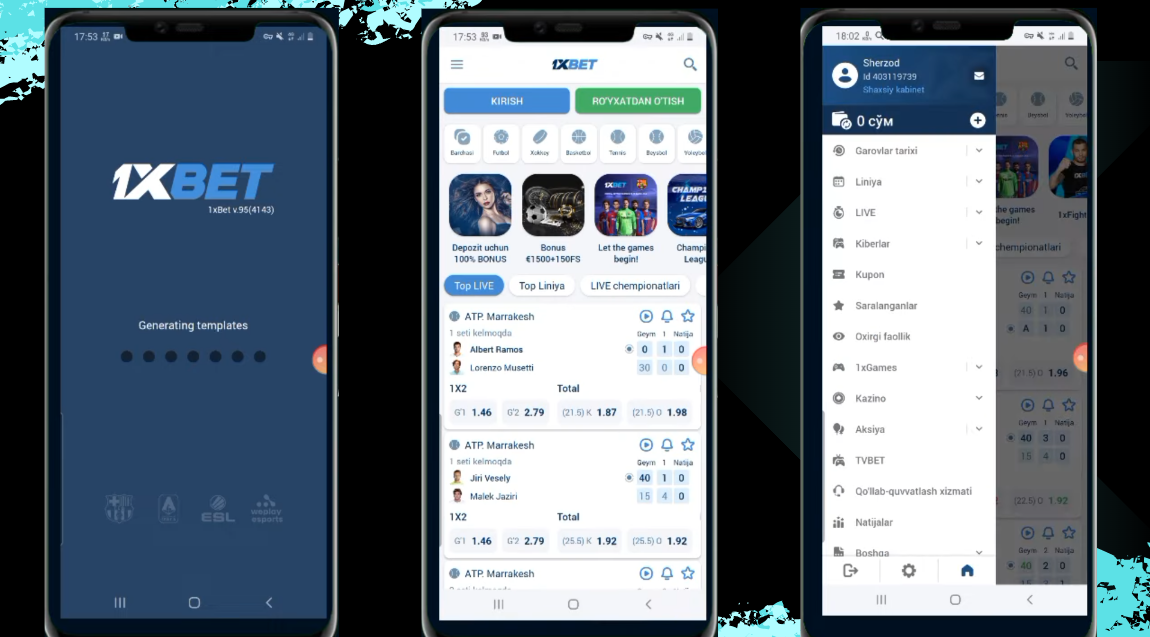
Payment handling reflects regional diversity in methods rather than imposing a single pipeline. Deposits and withdrawals route through locally familiar processors where possible, with cryptocurrency options supplementing traditional rails. Account verification requirements vary by jurisdiction and transaction threshold, with document submission handled in-app through camera integration.
The technical foundation matters for longevity. web app manifest standards influence how the native application handles offline states and notification delivery, even when full functionality demands connectivity. Push alerts for bet settlement, price movements, and promotional expiry arrive through Firebase or equivalent services, with granular controls in notification settings.

When native installation encounters barriers, the mobile website preserves most functionality through browser-based access. Progressive web app capabilities allow shortcut placement on home screens, though offline operation and native payment integrations diminish compared to the APK build.
Diagnosis and Recovery for Common Obstacles
Installation failures typically trace to three roots: incomplete downloads, signature mismatches, or permission misconfigurations. Corrupted APKs produce parsing errors before installation begins; re-downloading resolves this. Signature conflicts emerge when attempting updates from divergent sources, requiring clean reinstallation with account credentials to restore access.
Specific symptoms and responses:
- “App not installed” without elaboration: check storage space and Android version compatibility
- Installation silently aborts: verify the source permission grant targeted the correct initiating app
- Update refusal with certificate warning: uninstall and reinstall rather than forcing the update
- Launch crashes post-installation: clear app cache before considering data reset
- Geographic restriction messages: confirm regional availability rather than troubleshooting device settings

Performance degradation over time often stems from accumulated cache rather than app deterioration. Periodic cache clearing, available in Android’s app settings without data loss, restores responsiveness. For persistent issues, the uninstall-reinstall path remains definitive, though local preferences and cached credentials require re-entry.
The mobile website serves as permanent fallback when native installation proves impossible. Feature parity is substantial: betting markets, account management, and live streaming function through modern browsers, with the primary compromise being notification dependency on browser permission grants rather than native push services.
FAQ
Why does Android require per-source permission grants rather than a single toggle?
This granular model limits damage from compromised download channels. If one browser or file manager encounters malware, others remain restricted. You revoke rights per-source without affecting system-wide installation capabilities, and the audit trail of which app initiated each install improves forensic analysis.
How do I verify my download source remains consistent across years of updates?
Document your original acquisition path—browser used, file name pattern, any verification hashes checked. When updates appear, compare the offering source against this baseline before installing. Certificate mismatches trigger Android’s refusal; catching source divergence beforehand prevents forced reinstallation with data loss.
Should I keep unknown-source permissions enabled permanently?
Disable them for sources no longer in active use. The browser that fetched your initial APK needs no ongoing installation rights; revocation closes a theoretical attack surface without impairing the installed 1xBet app. Re-enable temporarily only when deliberately updating through that same channel.
What persists when I uninstall the 1xBet app?
Account data resides on operator servers, recoverable through re-authentication. Local data—including cached markets, notification preferences, and biometric login setup—typically removes with the app, though Android’s scoped storage may retain isolated files. Assume local customization loss and plan reconfiguration time.
How does the mobile website compare for long-term betting activity?
The website avoids installation friction and certificate management entirely, running within browser sandboxing. Trade-offs include dependent notification delivery, slightly reduced animation fluidity, and absence of native payment integration. For users prioritizing minimal device modification over maximum feature access, the web route ages comparably well.


The 1xBet App: Setup Choices That Age Well
A note before you begin: in some regions the 1xBet app does not appear in official stores due to local regulations. The instructions below cover the direct APK route, which remains fully functional when store access is restricted.
Preparing Your Device and Choosing Your Source
Installing third-party Android software demands a moment of deliberate setup. Your phone’s security model treats browsers and file managers as separate installation sources, each requiring independent permission grants. This granular approach protects you; it also means you must remember which app initiated your download, as revoking permissions later follows the same path.
Begin with these checks:
This preparation prevents the common trap of hunting through nested settings menus mid-installation. The permission architecture changed significantly across Android generations, so older guides may mislead. Current systems assign unknown-source rights per-application, not globally, and you retain the option to revoke these rights after installation completes.
Obtaining and Placing the APK File
Download practices shape your long-term security posture. The 1xBet Android package arrives as a single compressed file with the .apk extension, which your system unpacks during installation. Your download destination matters: browsers typically place files in a Downloads folder, while some file managers allow custom paths that simplify later location.
Follow this sequence:
The release channel and regional availability determine how the 1xbet android package mobile version distributions vary across different markets and update schedules. Cross-checking file hashes where provided adds verification depth, though this step sits outside basic setup. The core principle: treat your download source as a decision that persists across years of app updates.
Installation, Permissions, and Post-Setup Security
Android’s installation flow now guides you through source-specific permissions automatically. When you tap the APK, the system detects whether that source holds installation rights and offers a direct path to grant them if absent. This replaces the older global “unknown sources” toggle with precise, reversible controls.
Post-installation, consider your permission footprint. The browser that fetched your APK no longer needs installation rights; revoking this closes a potential vector without affecting the installed app. Similarly, the 1xBet application itself requests runtime permissions for notifications, location, and storage—grant these selectively based on your actual usage patterns rather than accepting defaults.
Update handling requires attention to certificate continuity. Android refuses updates signed by different certificates than the original installation, forcing an uninstall-reinstall cycle that may clear local data. Maintaining awareness of your original download source prevents this disruption. When updates arrive, verify the signing identity matches your baseline before applying.
Core Capabilities and Platform Architecture
The application presents a consolidated interface spanning multiple verticals without forcing navigation through separate installations. Sports betting occupies the primary real estate, with pre-match odds and live-event pricing accessible through shared search and filter tools. The live betting module updates prices in response to match events, with cash-out availability varying by sport and market liquidity.
Casino integration runs parallel rather than as an afterthought. Slots, table games, and live dealer streams pull from the same account balance and loyalty tracking. This unified wallet architecture eliminates the friction of inter-product transfers, though responsible gambling limits apply across all verticals simultaneously.
Payment handling reflects regional diversity in methods rather than imposing a single pipeline. Deposits and withdrawals route through locally familiar processors where possible, with cryptocurrency options supplementing traditional rails. Account verification requirements vary by jurisdiction and transaction threshold, with document submission handled in-app through camera integration.
The technical foundation matters for longevity. web app manifest standards influence how the native application handles offline states and notification delivery, even when full functionality demands connectivity. Push alerts for bet settlement, price movements, and promotional expiry arrive through Firebase or equivalent services, with granular controls in notification settings.
When native installation encounters barriers, the mobile website preserves most functionality through browser-based access. Progressive web app capabilities allow shortcut placement on home screens, though offline operation and native payment integrations diminish compared to the APK build.
Diagnosis and Recovery for Common Obstacles
Installation failures typically trace to three roots: incomplete downloads, signature mismatches, or permission misconfigurations. Corrupted APKs produce parsing errors before installation begins; re-downloading resolves this. Signature conflicts emerge when attempting updates from divergent sources, requiring clean reinstallation with account credentials to restore access.
Specific symptoms and responses:
Performance degradation over time often stems from accumulated cache rather than app deterioration. Periodic cache clearing, available in Android’s app settings without data loss, restores responsiveness. For persistent issues, the uninstall-reinstall path remains definitive, though local preferences and cached credentials require re-entry.
The mobile website serves as permanent fallback when native installation proves impossible. Feature parity is substantial: betting markets, account management, and live streaming function through modern browsers, with the primary compromise being notification dependency on browser permission grants rather than native push services.
FAQ
Why does Android require per-source permission grants rather than a single toggle?
This granular model limits damage from compromised download channels. If one browser or file manager encounters malware, others remain restricted. You revoke rights per-source without affecting system-wide installation capabilities, and the audit trail of which app initiated each install improves forensic analysis.
How do I verify my download source remains consistent across years of updates?
Document your original acquisition path—browser used, file name pattern, any verification hashes checked. When updates appear, compare the offering source against this baseline before installing. Certificate mismatches trigger Android’s refusal; catching source divergence beforehand prevents forced reinstallation with data loss.
Should I keep unknown-source permissions enabled permanently?
Disable them for sources no longer in active use. The browser that fetched your initial APK needs no ongoing installation rights; revocation closes a theoretical attack surface without impairing the installed 1xBet app. Re-enable temporarily only when deliberately updating through that same channel.
What persists when I uninstall the 1xBet app?
Account data resides on operator servers, recoverable through re-authentication. Local data—including cached markets, notification preferences, and biometric login setup—typically removes with the app, though Android’s scoped storage may retain isolated files. Assume local customization loss and plan reconfiguration time.
How does the mobile website compare for long-term betting activity?
The website avoids installation friction and certificate management entirely, running within browser sandboxing. Trade-offs include dependent notification delivery, slightly reduced animation fluidity, and absence of native payment integration. For users prioritizing minimal device modification over maximum feature access, the web route ages comparably well.